2026 Realistic 1z0-1104-25 Dumps Latest Oracle Practice Tests Dumps [Q16-Q30]

2026 Realistic 1z0-1104-25 Dumps Latest Oracle Practice Tests Dumps

1z0-1104-25 Dumps PDF – 1z0-1104-25 Real Exam Questions Answers

Oracle 1z0-1104-25 Exam Syllabus Topics:

Topic Details
Topic 1
  • Detecting, Remediating, and Monitoring OCI Resources: This section of the exam measures the skills of OCI Administrators and emphasizes monitoring and maintaining security posture across cloud resources. It focuses on the use of Cloud Guard, security zones, and the Security Advisor. Candidates also need to understand how to identify rogue users with threat intelligence, as well as use monitoring, logging, and event services for continuous visibility into performance and security.
Topic 2
  • OCI Security Introduction: This section of the exam measures the skills of Cloud Security Professionals and covers the basics of security in Oracle Cloud Infrastructure. It introduces the shared security responsibility model, the core principles of security design, and the use of foundational security services to secure deployments on OCI.
Topic 3
  • Protecting Data: This section of the exam measures the skills of Cloud Security Professionals and highlights data security practices in OCI. It tests knowledge of using the Key Management Service for encryption keys, managing secrets in the OCI Vault, and applying features of OCI Data Safe to ensure sensitive data remains protected.


NO.16 You have created a compartment TEST in your subscribed tenancy. Then, you created two groups, test1 and test2, and want the users in these groups to be able to manage all the resources in the TEST compartment.
Which policy would you use to achieve this?


NO.17 Which Oracle Data Safe feature enables the Internal test, development, and analytics teams to operate effectively while minimizing their exposure to sensitive data?


NO.18 Challenge 2 -Task 1
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the security zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
Review the architecture diagram, which outlines the resoures you’ll need to address the requirement:
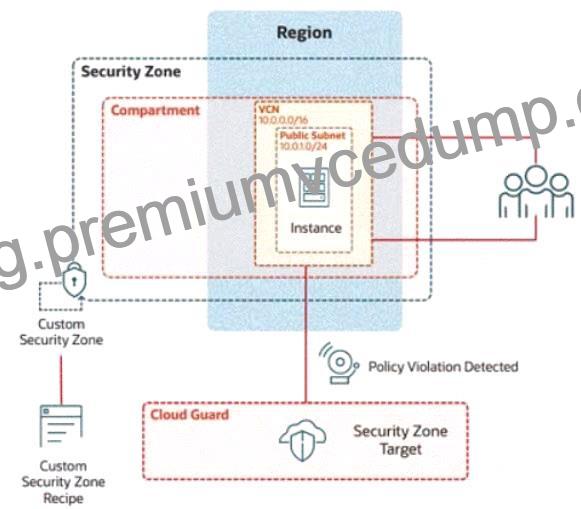
Preconfigured
To complete this requirement, you are provided with the following:
Access to an OCI tenancy, an assigned compartment, and OCI credentials
Required IAM policies
Task3: Create and configure a Virtual Cloud Network and Private Subnet
Createand configure virtual cloud Network (VCN) named IAD SP-PBT-VCN-01, with an internet Gateway and configure appropriate route rules to allow external connectivity.
Enter the OCID of the created VCN in the text box below.

NO.19 A company has deployed OCI Zero Trust Packet Routing (ZPR) to secure its network. They have two compute instances, VM1-01 and VM-02, in a public subnet. VM-01 is tagged with the security attribute app:
vm01, and VM-02 is tagged with app:vm02. The VCN is labeled with network:vcn01, The ZPR policy states:


“What is the expected outcome of this policy?


NO.20 Your organization needs to implement strong password policies for users in OCI.
Which of the following statements is TRUE about password policies in OCI IAM?


NO.21 Task 6: Create Load Balancer and Attach Certificate
Create a Load Balancer with the name PBT-CERT-LB-01 in subnet LB-Subnet-PBT-CERT-SNET-02 Create a Listener for the load balancer, where:
Name: PBT-CERT-LB_LTSN_01
Protocol: HTTPS
Port: 443
Attach the certificate PBT-CERT-01-<username> to the load balancer
Attach the security list PBT-CERT-LB-SL-01 to subnet LB-Subnet-PBT-CERT-SNET-02 See the solution below in Explanation.

NO.22 An OCI administrator notices that a compute instance running in the production compartment is unable to create Object Storage buckets using the OCI CLI command:
oci os bucket create –name mybucket –compartment-id <compartment_OCID> –auth instance_principal The error message returned states:
“NotAuthorizedOrNotFound: You are not authorized to perform this action.” The administrator verifies that the instance has Internet access and can reach OCI endpoints.
What then could be causing the issue?


NO.23 Task 3: Create a Master Encryption Key
Note: OCI Vault to store the key required by this task is created in the root compartment as PBI_Vault_SP Create an RSA Master Encryption Key (MEK), where:
Key name: PBT-CERT-MEK-01-<username>
For example, if your username is 99008677-lab.user01, then the MEK name should be PBT-CERT-MEK-
01990086771abuser01
Ensure you eliminate special characters from the user name.
Key shape: 4096 bits
Enter the OCID of the Master Encryption Key created in the provided text box:

NO.24 A company has implemented OCI IAM policies with multiple levels of compartments. A policy attached to a parent compartment grants “manage virtual-network-family” permissions. A policy attached to a child compartment grants “use virtual-network-family” permissions.

According to OCI IAM policy inheritance, how does the OCI IAM policy engine resolve the permissions for a user attempting to perform an operation that requires ‘manage’ permissions in the child compartment?


NO.25 Task 4: Create a Certificate Authority (CA)
Create a certificate authority, where:
CA name: PBT-CERT-CA-01-<username>
For example, if your username is 99008677-lab.user01, then the certificate authority name should be PBT- CERT-CA-01990086771abuser01 Ensure you eliminate special characters from the user name.
Common name: PBT-CERT-OCICA-01
Master Encryption Key: PBT-CERT-MEK-01 (created in the previous task)

NO.26 Challenge 2 -Task 1
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the security zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
Review the architecture diagram, which outlines the resoures you’ll need to address the requirement:

Preconfigured
To complete this requirement, you are provided with the following:
Access to an OCI tenancy, an assigned compartment, and OCI credentials
Required IAM policies
Task 4: Create a Public Subnet
Create a public subnet named IAD-SP-PBT-PUBSNET-01, within the VCN IAD-SP-PBT-VCN-01 use a CIDR block of 10.0.1.0/24 and configure the subnet to use the internet Gateway See the solution below in Explanation.

NO.27 Challenge 2
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the security zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
Review the architecture diagram, which outlines the resoures you’ll need to address the requirement:

Preconfigured
To complete this requirement, you are provided with the following:
Access to an OCI tenancy, an assigned compartment, and OCI credentials
Required IAM policies
Task 5: Provision a Compute Instance
Provision a compute instance in the IAD-SP-PBT-PUBSNET-01 public subnet, where:
Name IAD-SP-PBT-1-VM-01
image: Oracle Linux 8
Shape VM: Standard, A1, Flex
Enter the OCID of the created compute instance in the text box below.

NO.28 “A business has a hybrid cloud infrastructure with Oracle Linux instances running in OCI and on-premises.
They want to reduce the amount of bandwidth used when patching systems.
Which component of OS Management Hub can help to reduce the bandwidth usage for patching?


NO.29 An E-commerce company running on Oracle Cloud Infrastructure (OCI) wants to prevent accidental misconfigurations that could expose sensitive data. They need an OCI service that can enforce predefined security rules when creating or modifying cloud resources.
Which OCI service should they use?


NO.30 Task 5: Create a Certificate
Create a certificate, where:
Certificate name: PBT-CERT-01-<username>
For example, if your username is 99008677-lab.user01, then the certificate name should be PBT-CERT-
01990086771abuser01
Ensure you eliminate special characters from the user name.
Common name: PBT-CERT-OCICERT-01
Certificate Authority: PBT-CERT-CA-01 (created in the previous task)


1z0-1104-25 Premium Exam Engine pdf Download: https://www.premiumvcedump.com/Oracle/valid-1z0-1104-25-premium-vce-exam-dumps.html