CISA Dumps PDF New [2026] Ultimate Study Guide [Q122-Q145]

CISA Dumps PDF New [2026] Ultimate Study Guide

CISA Exam Dumps PDF Updated Dump from PremiumVCEDump Guaranteed Success

ISACA CISA Exam Syllabus Topics:

Section Weight Objectives
Information Systems Operations and Business Resilience 26% – Information Systems Operations

  • 1. Common Technology Components
  • 2. End-User Computing
  • 3. System Interfaces
  • 4. Job Scheduling and Production Process Automation
  • 5. IT Asset Management
  • 6. IT Service Level Management
  • 7. Database Management

– Business Resilience

  • 1. Data Backup, Storage, and Restoration
  • 2. Disaster Recovery Plan (DRP)
  • 3. System Resiliency
  • 4. Business Impact Analysis (BIA)
  • 5. Business Continuity Plan (BCP)
Information Systems Auditing Process 18% – Planning

  • 1. Risk-Based Audit Planning
  • 2. Types of Controls
  • 3. IS Audit Standards, Guidelines, and Codes of Ethics
  • 4. Types of Audits and Assessments
  • 5. Business Processes

– Execution

  • 1. Data Analytics
  • 2. Audit Project Management
  • 3. Reporting and Communication Techniques
  • 4. Sampling Methodology
  • 5. Quality Assurance and Improvement of the Audit Process
  • 6. Audit Evidence Collection Techniques
Protection of Information Assets 26% – Information Asset Security and Control

  • 1. Physical Access and Environmental Controls
  • 2. Privacy Principles
  • 3. Network and Endpoint Security
  • 4. Data Encryption and Encryption-Related Techniques
  • 5. Data Classification
  • 6. Information Asset Security Frameworks, Standards, and Guidelines
  • 7. Public Key Infrastructure (PKI)
  • 8. Identity and Access Management

– Security Event Management

  • 1. Information System Attack Methods and Techniques
  • 2. Security Testing Tools and Techniques
  • 3. Incident Response Management
  • 4. Evidence Collection and Forensics
  • 5. Security Monitoring Tools and Techniques
  • 6. Security Awareness Training and Programs
Information Systems Acquisition, Development and Implementation 12% – Information Systems Implementation

  • 1. System Migration, Infrastructure Deployment, and Data Conversion
  • 2. Configuration and Release Management
  • 3. Post-implementation Review
  • 4. Testing Methodologies

– Information Systems Acquisition and Development

  • 1. Business Case and Feasibility Analysis
  • 2. Control Identification and Design
  • 3. System Development Methodologies
  • 4. Project Governance and Management
Governance and Management of IT 18% – IT Management

  • 1. IT Resource Management
  • 2. Quality Assurance and Quality Management of IT
  • 3. IT Service Provider Acquisition and Management
  • 4. IT Performance Monitoring and Reporting

– IT Governance

  • 1. Enterprise Architecture
  • 2. Enterprise Risk Management
  • 3. IT Monitoring and Reporting Practices
  • 4. IT Investment and Allocation Practices
  • 5. Organizational Structure
  • 6. Maturity and Process Improvement Models
  • 7. IT Governance and IT Strategy
  • 8. IT-Related Frameworks
  • 9. IT Standards, Policies, and Procedures


Q122. An IS auditor finds that the process for removing access for terminated employees is not documented What is the MOST significant risk from this observation?


Q123. Which of the following is a PRIMARY benefit of using risk assessments to determine areas to be included in an audit plan?


Q124. Which of the following should an IS auditor recommend as a PRIMARY area of focus when an organization decides to outsource technical support for its external customers?


Q125. What is the most common purpose of a virtual private network implementation?


Q126. Due to advancements in technology and electronic records, an IS auditor has completed an engagement by email only. Which of the following did the IS auditor potentially compromise?


Q127. Which of the following is the BEST reason to implement a data retention policy?


Q128. Which of the following is the BEST source of organizational direction on when to use cloud services?


Q129. An IS auditor interviewing a payroll clerk finds that the answers do not support job descriptions and documented procedures. Under these circumstances, the IS auditor should:


Q130. The PRIMARY benefit of implementing a security program as part of a security governance framework is the:


Q131. An IS auditor performing a review of a newly purchased software program notes that an escrow agreement has been executed for acquiring the source code.
What is MOST important for the IS auditor to verify?


Q132. While planning a review of IT governance, the IS auditor is MOST likely to.


Q133. Which of the following is the GREATEST risk to the effectiveness of application system controls?


Q134. A transaction journal provides the information necessary for detecting unauthorized ___________ (fill in the blank) from a terminal.


Q135. During an audit of an enterprise that is dedicated to e-commerce, the IS manager states that digital signatures are used when receiving communications from customers. To substantiate this, an IS auditor must prove that which of the following is used?


Q136. Which of the following hardware devices relieves the central computer from performing network control, format conversion and message handling tasks?


Q137. An IS auditor is asked to review a large organization’s change management process. Which of the following practices presents the GREATEST risk?


Q138. Which of the following should be of MOST concern to an IS auditor during the review of a quality management system?


Q139. An IS auditor is mapping controls to risk for an accounts payable system What is the BEST control to detect errors in the system?


Q140. For effective IT governance, it is MOST important to have an independent reporting line for which of the following IT functions?


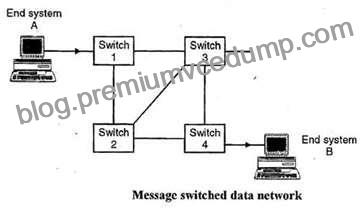
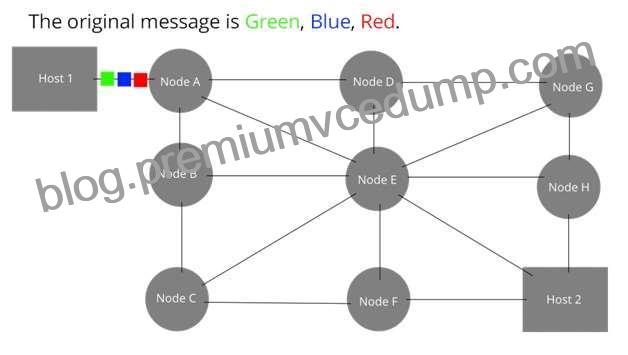
Q141. Identify the WAN message switching technique being used from the description presented below:
“Data is routed in its entirety from the source node to the destination node, one hope at a time. During
message routing, every intermediate switch in the network stores the whole message. If the entire
network’s resources are engaged or the network becomes blocked, this WAN switching technology stores
and delays the message until ample resources become available for effective transmission of the
message. “


Q142. .What is the PRIMARY purpose of audit trails?


Q143. Overall business risk for a particular threat can be expressed as:


Q144. Which of the following audit procedures would be MOST conclusive in evaluating the effectiveness of an e- commerce application system’s edit routine?


Q145. Which of the following is the MOST effective way for an IS auditor to identify unauthorized changes to the production state of a critical business application?


Pass Your ISACA Exam with CISA Exam Dumps: https://www.premiumvcedump.com/ISACA/valid-CISA-premium-vce-exam-dumps.html

Pass Your Exam Easily! CRISC Real Question Answers Updated on Feb 15, 2026 [Q744-Q762]

Pass Your Exam Easily! CRISC Real Question Answers Updated on Feb 15, 2026

Actual Questions Answers Pass With Real CRISC Exam Dumps

Please go to Pass Your Exam Easily! CRISC Real Question Answers Updated on Feb 15, 2026 [Q744-Q762] to view the test

The CRISC exam is intended for professionals who have experience in the field of IT risk management and are looking to advance their careers. CRISC exam covers a wide range of topics, including risk identification and assessment, risk response and mitigation, risk monitoring and reporting, and information systems control design and implementation. It is designed to test the candidate’s knowledge and skills in these areas and is considered one of the most prestigious certifications in the field of IT risk management. Passing CRISC exam demonstrates that the candidate has a deep understanding of the principles and practices of IT risk management and is capable of managing risks within an organization’s information systems.


New CRISC Dumps – Real ISACA Exam Questions: https://www.premiumvcedump.com/ISACA/valid-CRISC-premium-vce-exam-dumps.html

Actual Cybersecurity-Audit-Certificate Exam Recently Updated Questions with Free Demo [Q52-Q67]

Actual Cybersecurity-Audit-Certificate Exam Recently Updated Questions with Free Demo

Free ISACA Cybersecurity-Audit-Certificate Exam Questions Self-Assess Preparation

Please go to Actual Cybersecurity-Audit-Certificate Exam Recently Updated Questions with Free Demo [Q52-Q67] to view the test

Cybersecurity-Audit-Certificate Free Sample Questions to Practice One Year Update: https://www.premiumvcedump.com/ISACA/valid-Cybersecurity-Audit-Certificate-premium-vce-exam-dumps.html

Updated Feb-2024 100% Cover Real CISM Exam Questions Make Sure You 100% Pass [Q314-Q336]

Updated Feb-2024 100% Cover Real CISM Exam Questions Make Sure You 100% Pass

CISM dumps Accurate Questions and Answers with Free and Fast Updates

ISACA CISM certification exam consists of 150 multiple-choice questions that are designed to test an individual’s knowledge and understanding of the information security concepts and practices. CISM exam is conducted in a computer-based format and is available at various testing centers worldwide. CISM exam duration is four hours, and the passing score is 450 out of 800.

ISACA CISM (Certified Information Security Manager) Exam is a highly respected certification exam for professionals who are interested in advancing their careers in the field of information security management. CISM exam is designed to test the candidate’s knowledge and skills related to the management of information security programs, including risk management, incident management, compliance, and governance. The CISM certification is recognized globally and is highly valued by organizations looking for qualified professionals to manage their information security programs.


Please go to Updated Feb-2024 100% Cover Real CISM Exam Questions Make Sure You 100% Pass [Q314-Q336] to view the test

Real CISM Quesions Pass Certification Exams Easily: https://www.premiumvcedump.com/ISACA/valid-CISM-premium-vce-exam-dumps.html

[Feb 28, 2023] Pass CISM Review Guide, Reliable CISM Test Engine [Q55-Q69]

[Feb 28, 2023] Pass CISM Review Guide, Reliable CISM Test Engine

CISM Test Engine Practice Test Questions, Exam Dumps

ISACA Certified Information Security Manager CISM Exam

ISACA Certified Information Security Manager CISM Exam is related to Certified Information Security Manager CISM certification. This CISM Exam validates the ability to maintain and establish an information security governance framework and supporting processes to ensure that the information security strategy is aligned with organizational goals and objectives. Candidate must have the ability to manage information risk appropriately and program resources are managed responsibly. It also deals with the ability to ensure that organizational goals and objectives are supported by the information security program communicate managements directives and guide the development of standards, procedures, and guidelines and develop business cases to support investments in information security. Security Managers Industry Leaders and Industry Practitioners usually hold or pursue this certification and you can expect the same job roles after completion of this certification.


Please go to [Feb 28, 2023] Pass CISM Review Guide, Reliable CISM Test Engine [Q55-Q69] to view the test

100% Free CISM Daily Practice Exam With 188 Questions: https://www.premiumvcedump.com/ISACA/valid-CISM-premium-vce-exam-dumps.html