Get AZ-500 Products Practice Material for AZ-500 Exam Question Preparation [Q282-Q301]

Rate this post

Get AZ-500 Products Practice Material for AZ-500 Exam Question Preparation

Most Reliable Microsoft AZ-500 Training Materials

Microsoft AZ-500 Exam Syllabus Topics:

Section Weight Objectives
Manage security operations using Microsoft Defender for Cloud and Microsoft Sentinel (30–35%) 30-35% – Configure and manage Microsoft Defender for various resources

  • 1. Configure Microsoft Defender for Key Vault
  • 2. Configure Microsoft Defender for Resource Manager
  • 3. Configure Microsoft Defender for Containers
  • 4. Configure Microsoft Defender for DNS
  • 5. Configure Microsoft Defender for Storage

– Implement and manage Microsoft Sentinel

  • 1. Manage Microsoft Sentinel analytics rules
  • 2. Configure and manage automation rules and playbooks
  • 3. Plan and implement Microsoft Sentinel workspace architecture
  • 4. Investigate, hunt, and respond to incidents using Microsoft Sentinel
  • 5. Configure and manage Microsoft Sentinel data connectors
  • 6. Configure workbooks and dashboards

– Implement and manage Microsoft Defender for Cloud

  • 1. Implement and manage Defender for Servers and Defender for Endpoint integration
  • 2. Evaluate and remediate security posture
  • 3. Configure workflow automation using Defender for Cloud
  • 4. Configure and manage Defender for Cloud policies and plans
  • 5. Configure and manage regulatory compliance
Secure networking (20–25%) 20-25% – Implement and manage network security

  • 1. Implement and manage Azure Firewall
  • 2. Configure Azure DDoS protection
  • 3. Implement and manage Azure Firewall Manager
  • 4. Implement and manage network segmentation

– Plan and implement security for virtual networks

  • 1. Implement Azure Bastion and Just-in-Time (JIT) access
  • 2. Plan and implement user-defined routes (UDR)
  • 3. Secure private and public access to Azure services
  • 4. Plan and implement Network Security Groups (NSG) and Application Security Groups (ASG)

– Plan and implement security for public access to Azure resources

  • 1. Plan and implement Azure Front Door
  • 2. Plan and implement Azure Application Gateway
  • 3. Configure firewall settings on PaaS resources
  • 4. Plan and implement Web Application Firewall (WAF)

– Plan and implement security for private access to Azure resources

  • 1. Plan and implement private endpoints
  • 2. Plan and implement service endpoints
  • 3. Plan and implement private link services
Manage identity and access (15–20%) 15-20% – Manage Azure AD Governance

  • 1. Configure and manage privileged identity management (PIM)
  • 2. Implement and manage entitlement management
  • 3. Implement and manage access reviews

– Manage Microsoft Entra ID identities

  • 1. Create and manage users and groups
  • 2. Manage Microsoft Entra ID bulk operations
  • 3. Configure self-service password reset (SSPR)
  • 4. Manage guest and external accounts

– Manage Microsoft Entra authorization

  • 1. Interpret access assignments
  • 2. Configure Azure role-based access control (RBAC)
  • 3. Configure custom roles
  • 4. Configure Microsoft Entra Permissions Management

– Manage Microsoft Entra authentication

  • 1. Configure and manage authentication methods
  • 2. Configure Microsoft Entra Verified ID
  • 3. Implement and manage Microsoft Entra ID Protection
  • 4. Configure Microsoft Entra MFA
Secure compute, storage, and databases (20–25%) 20-25% – Plan and implement security for Azure SQL

  • 1. Configure and manage Microsoft Purview for sensitive data
  • 2. Implement and manage transparent data encryption (TDE)
  • 3. Configure Microsoft Defender for SQL
  • 4. Configure and manage Azure SQL firewall rules
  • 5. Implement and manage SQL database security
  • 6. Configure and manage dynamic data masking and data classification

– Plan and implement advanced security for compute

  • 1. Plan and implement security for Azure Container Registry
  • 2. Plan and implement security for Azure Kubernetes Service
  • 3. Configure and manage server-side encryption
  • 4. Plan and implement security for Azure virtual machines
  • 5. Plan and implement security for Azure Container Instances and Azure Container Apps
  • 6. Configure and manage Azure Disk Encryption

– Plan and implement security for storage

  • 1. Implement and manage Azure File Shares security
  • 2. Implement Azure Data Lake Storage security
  • 3. Configure access control for storage accounts
  • 4. Configure and manage storage shared access signatures (SAS)
  • 5. Configure storage account firewall and virtual networks
  • 6. Configure and manage Azure Storage encryption


Q282. You plan to use Azure Sentinel to create an analytic rule that will detect suspicious threats and automate responses.
Which components are required for the rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Q283. You create a new Azure subscription that is associated to a new Azure Active Directory (Azure AD) tenant.
You create one active conditional access policy named Portal Policy. Portal Policy is used to provide access to the Microsoft Azure Management cloud app.
The Conditions settings for Portal Policy are configured as shown in the Conditions exhibit. (Click the Conditions tab.)

The Grant settings for Portal Policy are configured as shown in the Grant exhibit. (Click the Grant tab.)

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q284. You have an Azure subscription that contains the following Azure App Service web app:
* Name: WebApp1
* App Service plan: Free
You need to configure WebApp1 to use an App Service managed certificate. The solution must minimize costs.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Q285. You have the Azure virtual machines shown in the following table.

Each virtual machine has a single network interface.
You add the network interface of VM1 to an application security group named ASG1.
You need to identify the network interfaces of which virtual machines you can add to ASG1.
What should you identify?


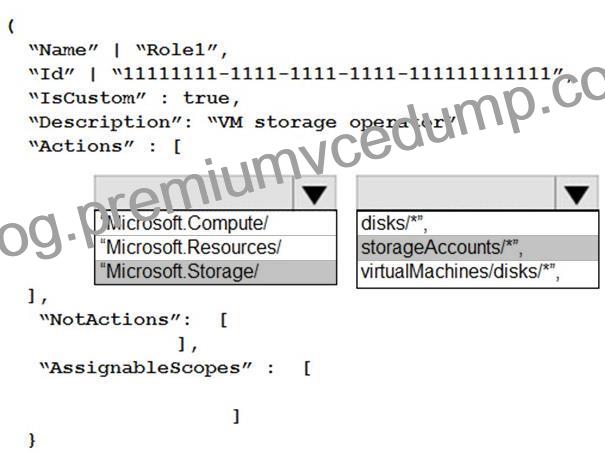
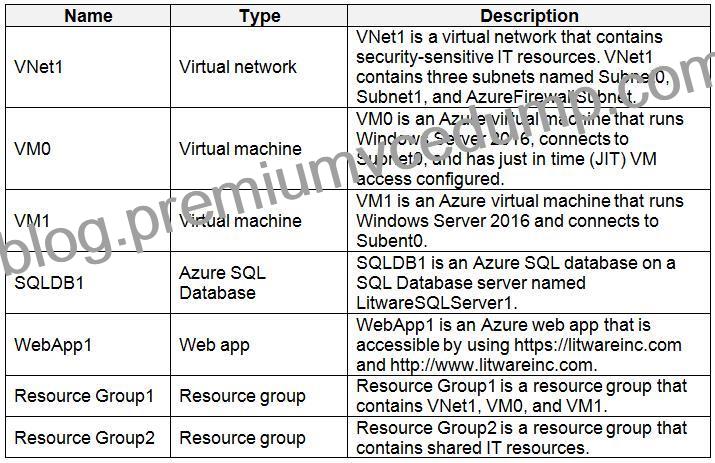
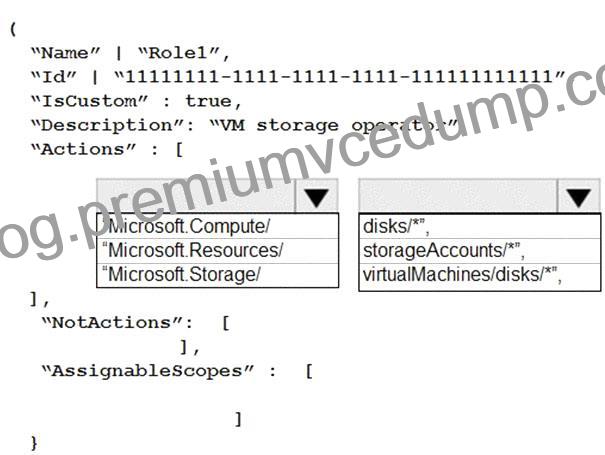
Q286. You need to create Role1 to meet the platform protection requirements.
How should you complete the role definition of Role1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q287. You need to deploy AKS1 to meet the platform protection requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
NOTE: More than one order of answer choices is correct. You will receive credit for any of the correct orders you select.

Q288. You are implementing an Azure Application Gateway web application firewall (WAF) named WAF1.
You have the following Bicep code snippet.

For each of The following statements, select Yes if the statement is true. Otherwise. Select No.
NOTE: Each correct selection is worth one point.

Q289. You plan to implement an Azure function named Function1 that will create new storage accounts for containerized application instances.
You need to grant Function1 the minimum required privileges to create the storage accounts. The solution must minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q290. You have an Azure subscription that contains the Azure Active Directory (Azure AD) resources shown in the following table.

You create the groups shown in the following table.
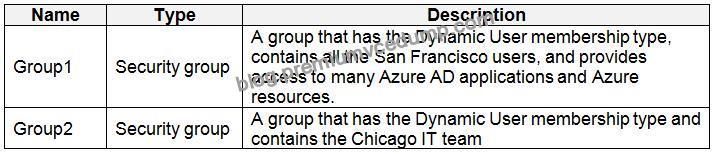
Which resources can you add to Group5 and Group6? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q291. You have an Azure subscription named Sub1 that contains the resource groups shown in the following table.

You create the Azure Policy definition shown in the following exhibit.

You assign the policy to Sub1.
You plan to create the resources shown in the following table.
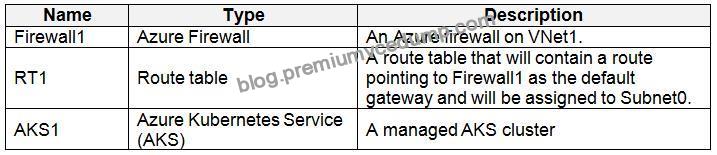
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q292. You need to ensure that you can meet the security operations requirements.
What should you do first?


Q293. You have an Azure Container Registry named Registry1.
You add role assignment for Registry1 as shown in the following table.

Which users can upload images to Registry1 and download images from Registry1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q294. You have an Azure AD tenant that contains the users shown in the following table.

You enable passwordless authentication for the tenant.
Which authentication method can each user use for passwordless authentication? To answer, drag the appropriate authentication methods to the correct users. Each authentication method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

Q295. You have an Azure subscription that contains an Azure Active Directory (Azure AD) tenant and a user named User1.
The App registrations settings for the tenant are configured as shown in the following exhibit.

You plan to deploy an app named App1.
You need to ensure that User1 can register App1 in Azure AD. The solution must use the principle of least privilege.
Which role should you assign to User1?


Q296. You have an Azure subscription that contains an app named App1. App1 has the app registration shown in the following table.

You need to ensure that App1 can read all user calendars and create appointments. The solution must use the principle of least privilege.
What should you do?


Q297. Your company uses cloud-based resources from the following platforms:
* Azure
* Amazon Web Services (AWS)
* Google Cloud Platform (GCP)
You plan to implement Microsoft Defender for Cloud.
On which platforms can you use Defender for Cloud to protect containers and storage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q298. You have an Azure Sentinel workspace that has an Azure Active Directory (Azure AD) data connector.
You are threat hunting suspicious traffic from a specific IP address.
You need to annotate an intermediate event stored in the workspace and be able to reference the IP address when navigating through the investigation graph.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Q299. You company has an Azure Active Directory (Azure AD) tenant named contoso.com.
You plan to create several security alerts by using Azure Monitor.
You need to prepare the Azure subscription for the alerts.
What should you create first?


Q300. You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.

Azure AD Privileged Identity Management (PIM) is enabled for the tenant.
In PIM, the Password Administrator role has the following settings:
Maximum activation duration (hours): 2
Send email notifying admins of activation: Disable
Require incident/request ticket number during activation: Disable
Require Azure Multi-Factor Authentication for activation: Enable
Require approval to activate this role: Enable
Selected approver: Group1
You assign users the Password Administrator role as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q301. You suspect that users are attempting to sign in to resources to which they have no access.
You need to create an Azure Log Analytics query to identify failed user sign-in attempts from the last three days. The results must only show users who had more than five failed sign-in attempts.
How should you configure the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


LATEST AZ-500 Exam Practice Material: https://www.premiumvcedump.com/Microsoft/valid-AZ-500-premium-vce-exam-dumps.html

Related Links: myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt www.stes.tyc.edu.tw